

By Nick Hoffmeyer, Head of Marketing at Bambi · Updated September 28, 2026 · 9 min read
Reviewed by Howard F. Berkowitz, a non-emergency medical transportation and paratransit expert with 30+ years in the industry (H&S Consulting).
HIPAA compliance for non-emergency medical transportation (NEMT) providers means following three federal rules, the Privacy Rule, the Security Rule, and the Breach Notification Rule, that govern how you collect, store, share, and dispose of any patient health information your dispatchers, drivers, and billing staff touch. In practice that means encrypted systems, role-based access, trained staff, secure client communication, and a documented retention and disposal process. Violations carry real financial and legal risk, so this guide covers what to do, not just what the law says.
NEMT companies handle protected health information (PHI) on nearly every trip: pickup and drop-off addresses tied to a medical appointment, diagnosis-adjacent details a facility shares ahead of a transport, insurance and Medicaid numbers, and sometimes care notes drivers need to do the job safely. Depending on how you operate, that can make an NEMT provider a HIPAA covered entity (for example, a provider that bills health plans electronically) or a business associate of a broker, health plan, or facility, whether or not the owner thinks of the company as a "healthcare business." This guide covers it in one place: the rules that apply, a compliance checklist, and the day-to-day practices for training, communication, and records.
This guide is general information, not legal advice. Talk to a healthcare attorney or compliance professional about your specific situation.
The Three HIPAA Rules That Apply to NEMT Providers
Every NEMT compliance program rests on three federal rules, and each one covers a different failure point.
The Privacy Rule controls who can see, use, and share PHI, and introduces the "minimum necessary" standard: staff should only access or share the PHI required for their specific task, not the full patient record. A dispatcher needs the pickup address and appointment time; they don't need the diagnosis behind the appointment.
The Security Rule requires administrative, physical, and technical safeguards for electronic PHI (ePHI), including a risk analysis, access controls, audit controls, and device security. Encryption is an "addressable" specification: you must implement it where reasonable and appropriate, or document why you use an equivalent alternative. This is the rule that governs your software, your phones, and your storage systems.
The Breach Notification Rule requires notifying affected individuals without unreasonable delay and no later than 60 days after discovering a breach of unsecured PHI. Breaches affecting 500 or more people must also be reported to HHS within that same 60-day window (and to prominent media when 500 or more residents of a state are affected). Smaller breaches can be logged and reported to HHS within 60 days after the end of the calendar year. State breach laws can add their own, sometimes shorter, deadlines, so check yours.
What Counts as PHI in an NEMT Trip
- Appointment times, pickup/drop-off addresses tied to a medical visit
- Diagnosis, treatment, or condition details shared by a facility or rider
- Insurance and Medicaid/Medicare policy numbers
- Names, addresses, and other identifiers linked to any of the above
Penalties for Non-Compliance
HHS adjusts HIPAA civil money penalties for inflation every year. The figures below reflect the adjustment HHS published in January 2026.
- Civil, Tier 1 (did not know and could not reasonably have known): $145 to $73,011 per violation
- Civil, Tier 2 (reasonable cause, not willful neglect): $1,461 to $73,011 per violation
- Civil, Tier 3 (willful neglect, corrected within 30 days): $14,602 to $73,011 per violation
- Civil, Tier 4 (willful neglect, not corrected within 30 days): $73,011 to $2,190,294 per violation
- Civil, calendar-year cap for identical violations: $2,190,294 (OCR has said it applies lower annual caps to Tiers 1 to 3)
- Criminal (knowingly obtaining or disclosing PHI): Up to $50,000 and 1 year in prison; up to $100,000 and 5 years under false pretenses; up to $250,000 and 10 years with intent to sell or cause harm
Real settlements show the range isn't theoretical. CVS Pharmacy agreed to pay $2.25 million in 2009 and Rite Aid $1 million in 2010, both over PHI such as prescription labels thrown into trash containers the public could reach. In 2019, the University of Rochester Medical Center paid $3 million after losing an unencrypted flash drive and having an unencrypted laptop stolen.
A HIPAA Compliance Checklist for NEMT Providers
Use this as a working checklist, not a one-time project. Compliance is maintained, not purchased.
- Complete a documented risk analysis and keep it current. The Security Rule requires one but sets no fixed schedule; many providers review it at least annually and after any major system or staffing change
- Set up role-based access controls, so drivers, dispatchers, and billing staff each see only what their job requires
- Encrypt ePHI at rest and in transit (see encryption standards below)
- Use multi-factor authentication for any system holding PHI (a widely recommended safeguard)
- Put Business Associate Agreements in place with every vendor that touches PHI
- Maintain audit logs of who accessed what PHI, and when
- Train every employee on HIPAA basics plus their specific role's requirements
- Document a breach response plan before you need one
- Set retention and disposal rules for both paper and digital records
- Run an internal audit on a fixed schedule (quarterly is a common cadence) and log findings
Encryption and Technical Standards
HIPAA does not name specific encryption algorithms. Common practice in healthcare software is AES-256 encryption for data at rest and TLS 1.2 or higher for data in transit, alongside role-based access and multi-factor authentication. Treat these as industry benchmarks rather than legal requirements, and document whatever standard you choose in your risk analysis.
Secure Client Communication Under HIPAA
Talking to riders, facilities, and family members is where PHI moves the most, and where the most avoidable mistakes happen.
Phone calls. Verify the caller's identity before sharing any PHI, take the call somewhere private, log key details in a secure system afterward, and get explicit consent before discussing a rider's trip or condition with a family member.
Email and messaging. HHS guidance says the Privacy Rule allows health care providers to email patients as long as they "apply reasonable safeguards when doing so," such as checking the address before sending and limiting the amount or type of information in unencrypted messages. If a patient asks not to receive unencrypted email, offer a more secure option, mail, or phone. In practice that means secure transmission and storage, access limited by role, and an audit trail, not open email threads with addresses and appointment details in plain text.
Family and emergency contacts. Verify the person's identity and authorization before sharing anything beyond pickup logistics, and apply the same minimum-necessary standard you'd use with facility staff.
Bambi's Driver App gives drivers their trip manifest and a direct message line to dispatch in one place, so trip details don't have to travel through personal text threads and sticky notes.
Training Your Team on HIPAA
Training works best when it's role-specific, not a single all-staff slideshow once a year.
- Drivers: Verbal discretion around riders and bystanders, securing documents in the vehicle, confidentiality during transport
- Dispatchers: Secure communication tools, minimum-necessary data sharing, protocol enforcement
- Administrative/billing staff: Policy enforcement, breach reporting chain, records and insurance data handling
Every employee needs the same baseline: what PHI is, the minimum-necessary standard, how to recognize a breach, and who to notify immediately if one happens. Layer role-specific modules on top of that baseline rather than repeating generic content for everyone.
HIPAA requires training for new staff within a reasonable time and again when policies change, plus ongoing security awareness, but it does not set a fixed refresher schedule. Annual refreshers are a common practice, and many broker contracts and state programs set their own training cadence, so check yours. A learning management system with short, role-specific modules and a quiz at the end beats a single long onboarding document nobody rereads.
HIPAA-Compliant Recordkeeping
Records fail HIPAA audits in two ways: keeping the wrong things too loosely, or getting rid of the right things the wrong way.
What to keep. Appointment schedules, insurance details, condition-related notes, and payment records tied to a rider all count as PHI and need the same protection as a medical chart.
How long to keep it. HIPAA requires you to keep your compliance documentation (policies, procedures, risk analyses, and similar records) for six years from the date it was created or last in effect, whichever is later. HIPAA itself does not set a retention period for trip or medical records; state law, your state Medicaid agency, and broker contracts (Modivcare, MTM, Alivi, Access2Care, and similar) do. Check all of them and follow the longest requirement.
How to store it. Digital records need encryption, strong unique credentials, monitoring, and backup redundancy. Physical records need locked storage, restricted room access, and a documented chain of custody.
How to dispose of it. HHS guidance lists shredding, burning, pulping, or pulverizing paper records so PHI is essentially unreadable and cannot be reconstructed. For electronic media, it lists clearing (overwriting), purging (degaussing), or physically destroying the media, not a simple delete. Log every disposal: date, method, and record type.
Recordkeeping Audit Checklist (Run Quarterly)
- Review data access controls and permissions
- Re-run a risk assessment
- Confirm employee training records are current
- Review the incident response and breach notification plan
- Verify encryption and access controls are actually in place, not just documented
- Spot-check employee access logs for anything unusual
Working With Third-Party Vendors
Any vendor that touches PHI, your dispatch software, a records-destruction company, a billing clearinghouse, needs a signed Business Associate Agreement and a periodic risk review. This applies to your NEMT software provider too: ask any vendor how they encrypt data, who has access, and how they'd notify you of a breach before you sign.
Frequently Asked Questions
What are the three main HIPAA rules NEMT providers need to follow? The Privacy Rule (who can access PHI and the minimum-necessary standard), the Security Rule (technical, physical, and administrative safeguards for electronic PHI), and the Breach Notification Rule (notifying affected individuals within 60 days of discovering a breach, and reporting it to HHS on the timeline set by its size).
Does a small NEMT company really need to worry about HIPAA? Yes. Any company handling PHI, appointment details, diagnosis-adjacent notes, insurance numbers, tied to a healthcare visit can fall under HIPAA as a covered entity or business associate, regardless of fleet size. HIPAA's rules apply to small organizations as well as hospitals, and brokers and health plans typically require their transportation providers to protect PHI by contract.
What HIPAA training do NEMT drivers need? Drivers need the same baseline as every employee (what PHI is, minimum necessary, breach recognition) plus role-specific training on verbal discretion, securing documents in the vehicle, and maintaining confidentiality in front of other riders or bystanders.
How long do NEMT providers have to keep patient records? HIPAA requires six years for compliance documentation, but it does not set a retention period for trip or medical records. State law, state Medicaid agencies, and broker contracts do, and they can require longer. Check all of them before setting a company-wide policy.
What happens if a HIPAA breach occurs? Secure the affected system immediately, document what happened and when, notify your privacy officer, and report to HHS and affected individuals within the required window if the breach meets reporting criteria: individuals no later than 60 days after discovery, and HHS within 60 days for breaches affecting 500 or more people. Delaying notification is its own separate risk.
Can NEMT providers text or email riders and still be HIPAA-compliant? Yes, with reasonable safeguards: encrypted transmission and storage, identity verification, and sharing only the minimum information needed. HHS guidance says providers may email patients if they "apply reasonable safeguards when doing so."
Build Compliance Into How You Run Trips, Not On Top Of It
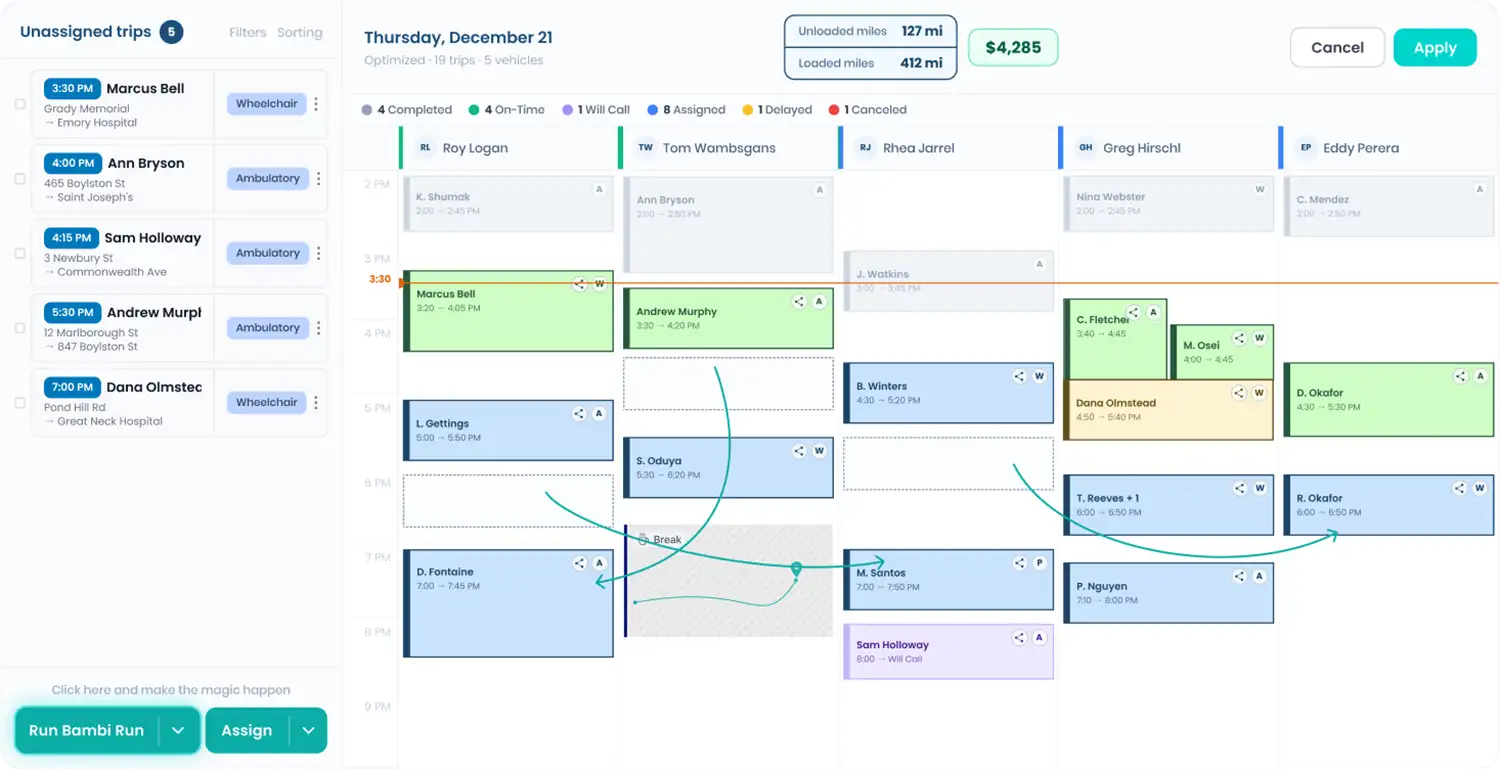
The fleets that stay out of HIPAA trouble aren't the ones with the thickest policy binder, they're the ones where trip data lives in the software dispatchers and drivers already use every day, instead of in personal texts and spreadsheets. Bambi signs a Business Associate Agreement with customers as part of its order form. Run Bambi Run assigns trips in one click, drivers work from their manifest and message dispatch in the Driver App, and Get Paid keeps GPS-stamped, signature-verified trip records with audit-ready logs. Bambi is $69 per vehicle per month, flat, with no contracts. See pricing.
About the author: Nick Hoffmeyer is Head of Marketing at Bambi, the AI-powered dispatch and scheduling platform for non-emergency medical transportation (NEMT) providers. He leads Bambi's growth, SEO, and content strategy and works with NEMT owner-operators every day on the systems that help fleets run more trips with less stress. Connect with Nick on LinkedIn.